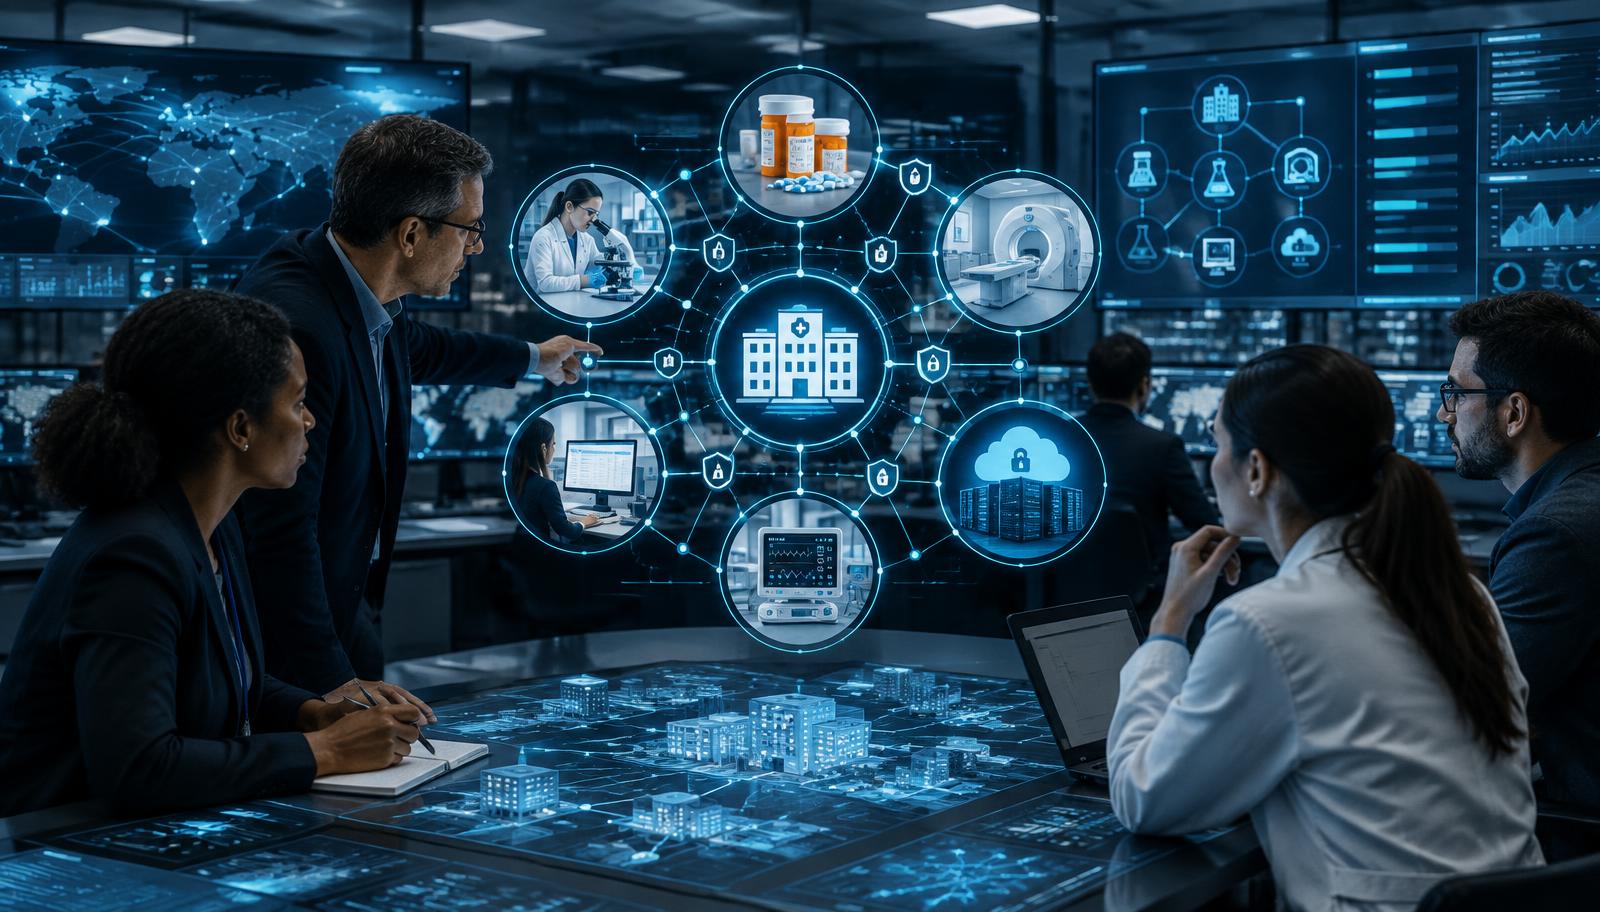
Critical hospital services depend on technology and providers outside the hospital. A supply chain intelligence program reveals which vendor disruptions could affect care first.
A hospital can secure its own perimeter and still lose a critical service because a supplier, cloud platform, laboratory partner, claims processor, pharmacy system, or medical device vendor was compromised.
The healthcare supply chain is not only a procurement concern. It is an operational dependency map. Cyber threat intelligence gives hospitals a way to monitor that map for changes that could affect care delivery.
Begin with critical services, not a vendor spreadsheet
Traditional third-party programs often start with questionnaires and contract records. Those are necessary, but they rarely show which supplier failure would matter first during a real incident.
Start with essential services:
- Medication ordering and dispensing
- Laboratory orders and results
- Imaging acquisition and viewing
- Electronic health records
- Patient registration and scheduling
- Claims, billing, and payment
- Blood products and specialized supplies
- Medical device maintenance
- Cloud communications and identity
- Ambulance, transfer, and referral coordination
For each service, identify the technology, data flows, vendors, subcontractors, remote access, recovery assumptions, and manual alternatives.
NIST defines cyber supply chain risk management as identifying, assessing, and mitigating risk across the life cycle of interconnected technology products and services (NIST C-SCRM overview). For healthcare, that life cycle must also be connected to clinical consequence.
Write supplier-focused intelligence requirements
A useful requirement asks a decision question. Examples include:
- Which critical vendors are being targeted by ransomware groups active in healthcare?
- Which internet-facing products used by our suppliers are under active exploitation?
- Which vendors have experienced credential leaks, impersonation, or new extortion claims?
- Which remote support pathways could reach clinical networks?
- Which single providers support multiple essential services?
- Which fourth parties create concentrated risk across several vendors?
These questions guide collection toward information the hospital can act on.
Collect signals before the disruption
Supplier intelligence can draw from official advisories, sector sharing groups, vendor notices, breach disclosures, vulnerability catalogs, domain monitoring, credential exposure, ransomware leak sites, and changes to a vendor's public infrastructure.
No single signal proves compromise. The analyst's job is to combine them and state confidence clearly.
A useful alert might say: “A critical laboratory vendor uses a product newly listed as exploited in the wild. The affected service is internet-facing. The vendor has not confirmed its patch status. Loss of connectivity would delay results at three facilities. Recommend escalation to the vendor, temporary monitoring of the integration, and validation of downtime procedures.”
That is more useful than forwarding the advisory alone.
Put intelligence into contracts and reviews
Supplier contracts should support the questions defenders will need answered during an incident. Requirements may include:
- Timely notification of security incidents that affect hospital services or data
- Disclosure of material subcontractor dependencies
- Clear ownership of remote access
- Supported software and firmware life cycles
- Vulnerability and patch communication
- Participation in incident exercises
- Recovery objectives tied to clinical needs
- A method to exchange indicators and investigation findings
Threat intelligence can improve these terms by showing how attackers currently exploit vendor relationships.
Plan for unavailable answers
During a widespread incident, vendors may be slow to respond. Hospitals should define actions that do not depend on immediate confirmation:
- Increase monitoring around the integration.
- Restrict unnecessary vendor access.
- Preserve logs and baseline traffic.
- Confirm manual or alternate workflows.
- Establish clinical thresholds for service isolation.
- Coordinate communications across facilities.
The decision to disconnect a supplier cannot be made by cybersecurity alone when patient care depends on the connection.
Track concentration and cascading impact
A vendor may appear low risk when reviewed in isolation but become critical because it supports several facilities or services. Maintain a view of shared technology, common remote access providers, and dependencies that could fail together.
NIST's Cybersecurity Framework 2.0 supply chain guide emphasizes collaboration and communication across the enterprise when managing supplier risk (NIST SP 1305). In a hospital, that collaboration must include clinical operations, procurement, legal, continuity, privacy, and technology teams.
Intelligence makes third-party risk continuous
A yearly assessment describes a vendor at one point in time. Threat intelligence tracks how that risk changes.
The goal is not perfect awareness of every supplier. It is enough warning and context to protect the services that patients depend on. When a vendor becomes the next incident, the hospital should already know what it supports, how compromise might spread, and what safe alternatives exist.