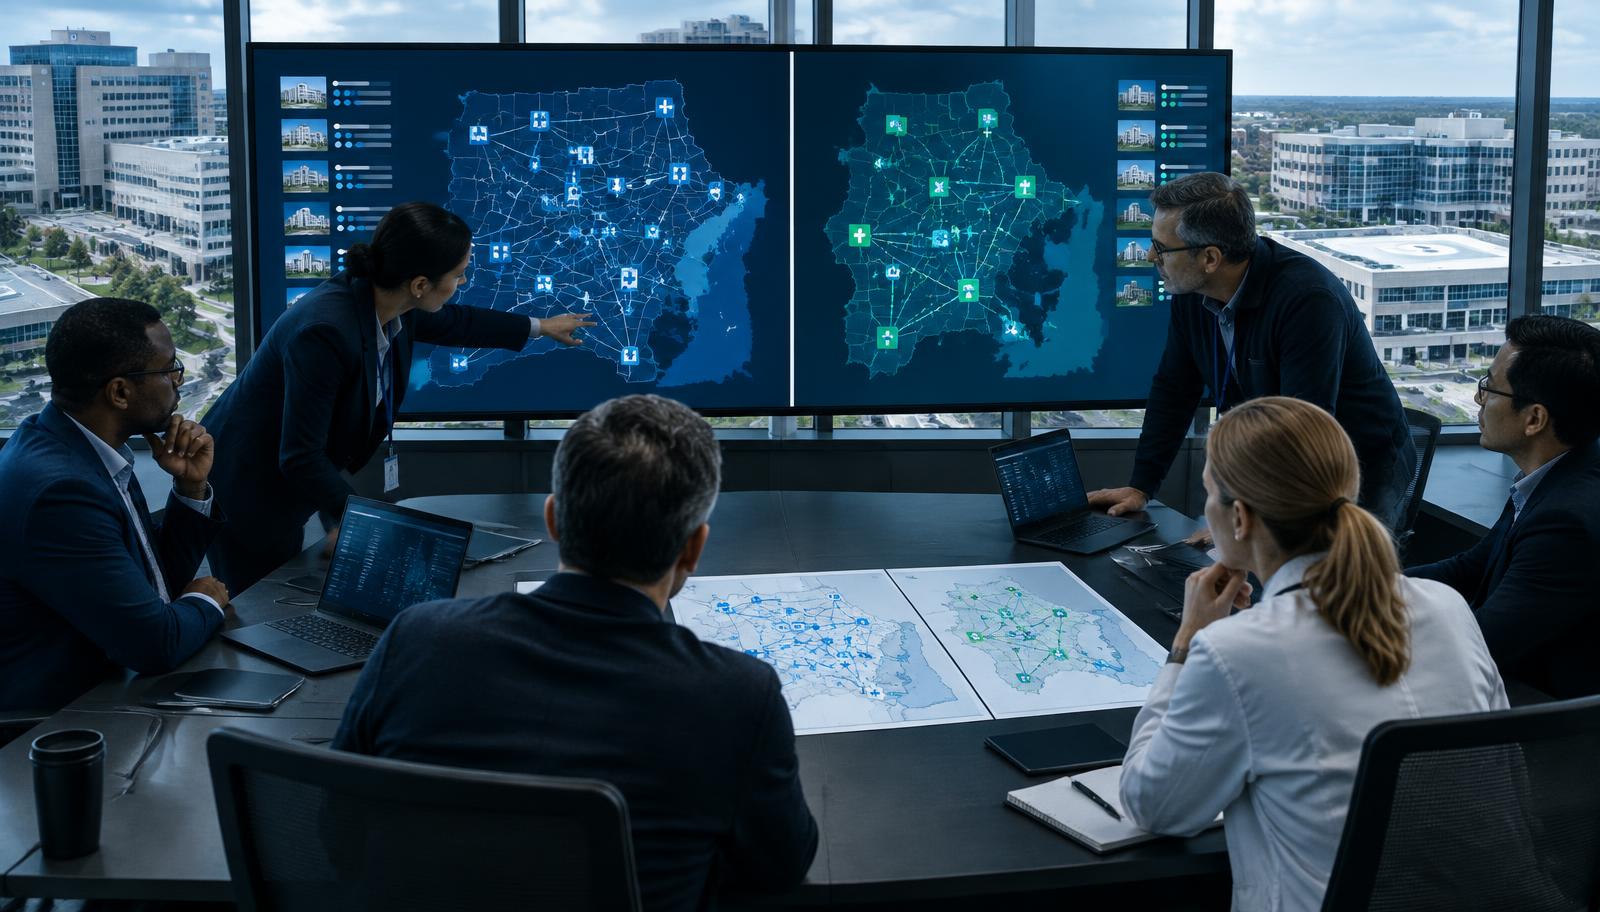
Health system acquisitions connect networks, identities, vendors, and clinical services. CTI helps integration teams find inherited exposure before it becomes shared risk.
A healthcare acquisition changes more than ownership. It connects two histories of technology decisions, vendor relationships, security controls, clinical workflows, and unresolved risk.
The acquired organization may bring unsupported medical devices, exposed remote access, dormant accounts, unknown internet assets, or a recent compromise that has not yet been discovered. Once environments are connected, local risk can become system-wide risk.
Cyber threat intelligence gives merger and acquisition teams a way to investigate the external threat picture, prioritize technical validation, and pace integration around evidence rather than deadlines alone.
Intelligence should begin before network connection
Due diligence often relies on questionnaires, policy documents, audit findings, and leadership interviews. These sources describe what the organization believes about itself. CTI adds an outside view.
Before integration, assess:
- Internet-facing systems and domains
- Exposed credentials associated with the organization
- Known ransomware or extortion claims
- Brand impersonation and lookalike domains
- Vulnerabilities in externally visible technology
- Third parties with privileged access
- Publicly reported incidents and regulatory disclosures
- Threat actors known to target the organization's region, specialty, or research
None of these signals should be treated as proof without validation. They are leads that shape technical diligence.
Map the inherited clinical attack surface
Healthcare integration must account for assets that conventional discovery may miss:
- Imaging and laboratory systems
- Medical device management platforms
- Pharmacy and medication dispensing systems
- Building automation and facilities controls
- Research environments
- Physician practice networks
- Telehealth and patient portals
- Vendor remote support
- Cloud applications managed outside central IT
Ask not only “what exists?” but “what must communicate after close?” Every connection creates a trust decision.
Separate identity before combining it
Identity integration is often accelerated because employees need access to shared applications. That urgency can create excessive trust.
Before federation or directory consolidation, identify:
- Privileged accounts and group memberships
- Stale workforce and contractor accounts
- Service accounts with unknown owners
- Authentication methods and exceptions
- Help desk reset procedures
- Vendor and affiliate identities
- Accounts shared across clinical workflows
Use intelligence about credential theft, social engineering, and valid-account abuse to decide where stronger controls and monitoring are required before trust is extended.
Score risk by pathway and consequence
A long list of findings can overwhelm integration teams. Group them into attack paths:
- Initial access through exposed services, phishing, credentials, or vendors
- Privilege escalation through identity weaknesses
- Movement into shared infrastructure or clinical networks
- Access to sensitive data or critical services
- Disruption, extortion, espionage, or fraud
Then connect each path to clinical and operational consequence. A weakness that can reach an essential service should rank above a similar weakness isolated to a disposable environment.
Use integration gates
Network integration should occur in stages with evidence-based gates. A gate might require:
- Critical internet exposures remediated
- Privileged identities reviewed
- Endpoint and network visibility confirmed
- Vendor access inventoried
- Essential clinical dependencies documented
- Backup and recovery procedures tested
- High-risk indicators investigated
- An incident escalation path agreed upon
If the evidence does not support full trust, use segmentation, monitored access, and limited data exchange until the risk is reduced.
Keep watching after close
The first months after an acquisition are attractive to attackers. Teams are changing systems, employees expect unusual login prompts, vendors are reconnecting, and ownership can be unclear.
Create a temporary intelligence requirement set for the integration period:
- Are credentials tied to either organization appearing in new exposure?
- Are threat actors discussing the merger, brands, or executives?
- Are lookalike domains or fraudulent communications increasing?
- Are new remote tools or data transfers appearing?
- Are known actor techniques visible across the connection boundary?
Brief both security teams together so local context is not lost.
Make cyber intelligence part of deal value
Unrecognized cyber risk can change integration cost, timing, insurance, contract terms, and leadership attention. The purpose of CTI is not to stop every transaction. It is to reveal material uncertainty early enough to manage it.
A safe healthcare merger treats connectivity as a clinical risk decision. Intelligence helps leaders understand what they are inheriting, which pathways require containment, and when the combined organization is ready to trust itself.